An AI agent that keeps working after you close the chat changes the risk model as much as it changes the productivity model.
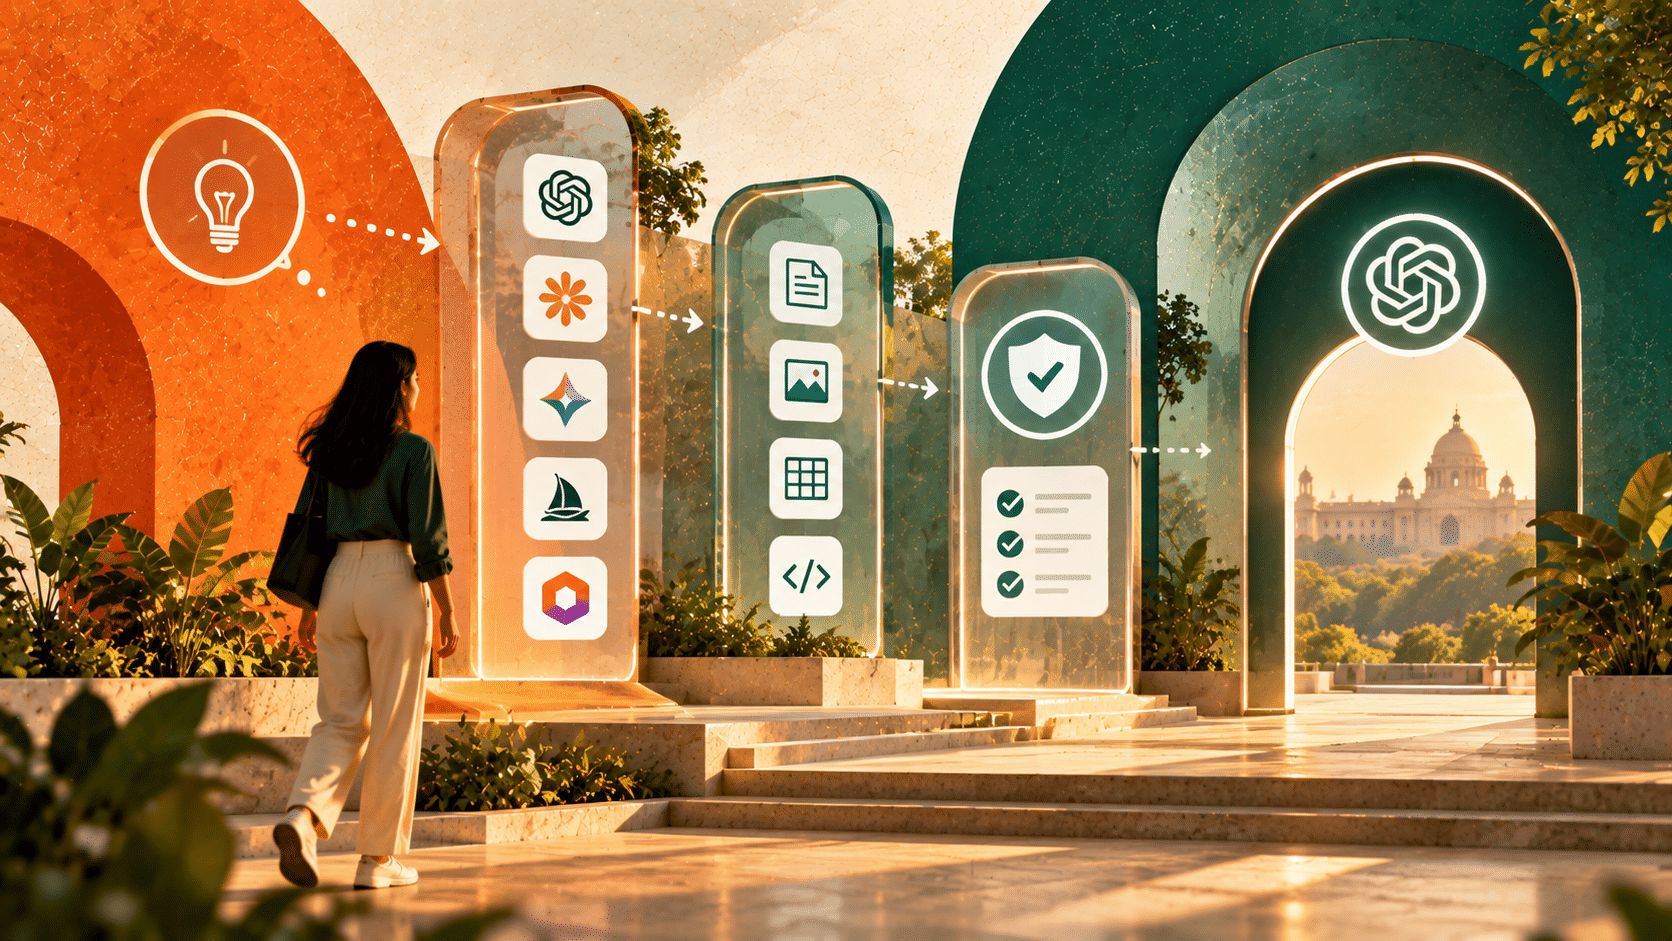
OpenAI introduced dots on September 29 always-on agents powered by GPT-6 Astra, with their own cloud computer and the ability to connect to apps through plugins. The product is rolling out gradually rather than appearing for every user at once. The practical question is simple which actions can happen without you watching?
Build the approval map first
Take one recurring workflow and label every step Read, Prepare, Act or Approve. Let the agent handle reading and preparation first. Put external communication, spending, publishing, deleting data and permission changes behind explicit approval.
This turns a vague instruction such as “manage this project” into something you can inspect. Reading a calendar is not the same permission as moving a meeting. Drafting a reply is not the same as sending it. Preparing an invoice is not the same as approving payment.
Start with a boring job
A useful first dot should not be “run my business.” Try a bounded outcome such as preparing a morning brief from your calendar, project updates and selected files. You can inspect the output before expanding access.
Good first jobs have three properties they happen repeatedly, the correct output is easy for you to recognise, and a mistake is reversible. Meeting preparation, status summaries and document assembly are better starting points than financial commitments or unsupervised client communication.
Use the smallest useful permission set
If the agent can complete 80 percent of the value with read-only access, start there. Add write access only when the missing action is genuinely worth the extra risk. This makes failures easier to diagnose and prevents convenience from quietly expanding into authority.
Map this workflow into Read, Prepare, Act and Approve steps. Recommend what an always-on agent may do independently, what it may draft but not send, and what must stop for my approval. Flag any step involving money, credentials, deletion, publishing, permissions or sensitive data. Suggest the minimum app permissions needed for the first version.
Keep an audit trail
If an agent can act while you are away, you need to be able to see what it did, what information it used and where it stopped for confirmation. A useful activity record should let you reconstruct the sequence rather than simply report that the task is complete.
Review the first few runs manually. Look for unnecessary app access, repeated corrections, actions you expected to approve and places where the agent interpreted an ambiguous instruction too broadly.
Know when to expand
Only give the agent a wider job after the narrow workflow is predictable. A practical rule is to run the bounded version several times, record failures and tighten instructions before adding another app or another type of action.
Review the agent like a new process
After the first week, do not ask only whether the agent saved time. Check how often it needed correction, whether it accessed more information than necessary, how many approval stops it triggered and whether you could understand its activity log. If the workflow is still unpredictable, narrow the scope before adding more autonomy. Reliability should earn permission rather than permission being granted upfront.
Have an exit plan
Know how to pause the agent, revoke app access and recover the source information it used. An always-on workflow should never depend on remembering where every permission was granted. Document the connected apps and the quickest way to stop activity before you need that information urgently.
Human boundary
Always-on should not mean unlimited authority. Keep explicit approval around money, credentials, irreversible changes, external publishing and consequential communication. The point of an agent is to return attention, not remove accountability.
Sources
OpenAI – Introducing dots, September 29, 2026
OpenAI – ChatGPT release notes